Short answer
Do not choose Search online for a private path. That action immediately sends the selected item's full path in a Google query. Inspect the file locally, then type a separate search using only a safe file name, publisher, or locally calculated hash.
When to use this method
Use this method when you do not recognize a large file and its folder path contains a user name, client name, project name, or another private detail.
Before you start
Do not open or run an unknown file just to identify it. Start with Properties, its folder and Windows Security. A hash lookup searches a locally calculated fingerprint without sending the file. A file upload sends the contents.
Local research and online search What stays on the PC and what the Search online action can disclose.
- Network behavior
- Normal scanning does not upload the file list. Search online places the selected full path in a Google query, so a manual sanitized search is the safer choice for identifying paths.
- Important limit
- C:\Users\Name\Client-X\case-notes.db reveals more than the base name. A hash lookup avoids that path and the file bytes; a sample upload discloses the content itself.
Investigate from local evidence first
Open the containing folder
Inspect the parent folder without opening or running the unknown file. You should see which application or project may own it.
Read Properties
Record the extension, size, dates, version information, publisher, and digital-signature status. You should have local clues before searching.
Write a safe query yourself
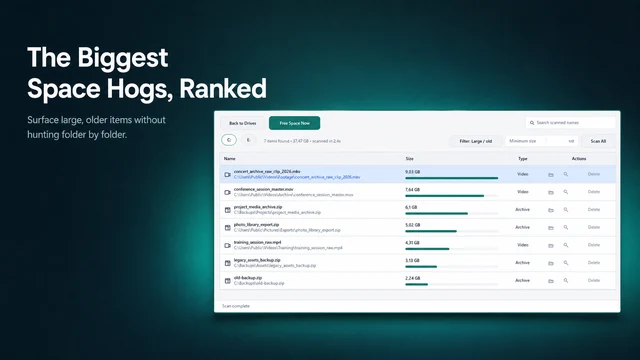
Do not click the magnifying-glass Search online action. Remove user names, client names, project titles, drive labels, and folders. Search something like example.dll Example Publisher, not the full path.
Use a hash when it helps
Calculate SHA-256 locally and search only its 64 characters. A hash does not send the file bytes, but it can identify a file already known to the search service. Uploading the file is a separate decision that sends its contents.
Use the owner's action
Use the application's uninstall, archive, or cleanup workflow. Use Windows Security to quarantine a suspicious file. You should not delete it based only on its size or name.
Research privacy risks
- Clicking Search online before reviewing the generated query
- Posting a client or username from the full path
- Uploading private file content when a hash lookup was intended
- Deleting a signed component based on size alone
Checkpoint: Disclosure checks
- Inspect properties without launching the file.
- Write a query that contains no folder path.
- Distinguish a hash search from a file upload.
- Use the owning app or Windows Security for the next action.
Osenpa Disk Analyzer
Inspect an unknown large item locally and understand exactly what the optional online-search action would disclose.